

[Apr 30, 2024] CS0-003 Exam Dumps - 100% Marks In CS0-003 Exam!
Exam Dumps Use Real CompTIA Cybersecurity Analyst Dumps With 305 Questions!
NEW QUESTION # 23
An organization was compromised, and the usernames and passwords of all em-ployees were leaked online.
Which of the following best describes the remedia-tion that could reduce the impact of this situation?
- A. System hardening
- B. Multifactor authentication
- C. Password changes
- D. Password encryption
Answer: B
Explanation:
Multifactor authentication (MFA) is a security method that requires users to provide two or more pieces of evidence to verify their identity, such as a password, a PIN, a fingerprint, or a one-time code. MFA can reduce the impact of a credential leak because even if the attackers have the usernames and passwords of the employees, they would still need another factor to access the organization's systems and resources. Password changes, system hardening, and password encryption are also good security practices, but they do not address the immediate threat of compromised credentials.
References: CompTIA CySA+ Certification Exam Objectives, [What Is Multifactor Authentication (MFA)?]
NEW QUESTION # 24
A systems administrator receives reports of an internet-accessible Linux server that is running very sluggishly. The administrator examines the server, sees a high amount of memory utilization, and suspects a DoS attack related to half-open TCP sessions consuming memory. Which of the following tools would best help to prove whether this server was experiencing this behavior?
- A. Nmap
- B. EDR
- C. TCPDump
- D. SIEM
Answer: C
Explanation:
TCPDump is the best tool to prove whether the server was experiencing a DoS attack related to half-open TCP sessions consuming memory. TCPDump is a command-line tool that can capture and analyze network traffic, such as TCP, UDP, and ICMP packets. TCPDump can help the administrator to identify the source and destination of the traffic, the TCP flags and sequence numbers, the packet size and frequency, and other information that can indicate a DoS attack. A DoS attack related to half-open TCP sessions is also known as a SYN flood attack, which is a type of volumetric attack that aims to exhaust the network bandwidth or resources of the target server by sending a large amount of TCP SYN requests and ignoring the TCP SYN-ACK responses. This creates a backlog of half-open connections on the server, which consume memory and CPU resources, and prevent legitimate connections from being established12. TCPDump can help the administrator to detect a SYN flood attack by looking for a high number of TCP SYN packets with different source IP addresses, a low number of TCP SYN-ACK packets, and a very low number of TCP ACK packets34. Reference: SYN flood DDoS attack | Cloudflare, What is a SYN flood attack and how to prevent it? | NETSCOUT, TCPDump - A Powerful Tool for Network Analysis and Security, How to Detect a SYN Flood Attack with TCPDump
NEW QUESTION # 25
A security analyst needs to mitigate a known, exploited vulnerability related not tack vector that embeds software through the USB interface. Which of the following should the analyst do first?
- A. Write a removable media policy that explains that USBs cannot be connected to a company asset.
- B. Review logs to see whether this exploitable vulnerability has already impacted the company.
- C. Check configurations to determine whether USB ports are enabled on company assets.
- D. Conduct security awareness training on the risks of using unknown and unencrypted USBs.
Answer: C
Explanation:
USB ports are a common attack vector that can be used to deliver malware, steal data, or compromise systems.
The first step to mitigate this vulnerability is to check the configurations of the company assets and disable or restrict the USB ports if possible. This will prevent unauthorized devices from being connected and reduce the attack surface. The other options are also important, but they are not the first priority in this scenario.
References:
* CompTIA CySA+ CS0-003 Certification Study Guide, page 247
* What are Attack Vectors: Definition & Vulnerabilities, section "How to secure attack vectors"
* Are there any attack vectors for a printer connected through USB in a Windows environment?, answer by user "schroeder"
NEW QUESTION # 26
An analyst is reviewing a vulnerability report for a server environment with the following entries:
Which of the following systems should be prioritized for patching first?
- A. 54.74.110.228
- B. 54.74.110.26
- C. 10.101.27.98
- D. 54.73.225.17
Answer: A
Explanation:
The system that should be prioritized for patching first is 54.74.110.228, as it has the highest number and severity of vulnerabilities among the four systems listed in the vulnerability report. According to the report, this system has 12 vulnerabilities, with 8 critical, 3 high, and 1 medium severity ratings. The critical vulnerabilities include CVE-2019-0708 (BlueKeep), CVE-2019-1182 (DejaBlue), CVE-2017-0144 (EternalBlue), and CVE-2017-0145 (EternalRomance), which are all remote code execution vulnerabilities that can allow an attacker to compromise the system without any user interaction or authentication. These vulnerabilities pose a high risk to the system and should be patched as soon as possible.
NEW QUESTION # 27
A company's security team is updating a section of the reporting policy that pertains to inappropriate use of resources (e.g., an employee who installs cryptominers on workstations in the office). Besides the security team, which of the following groups should the issue be escalated to first in order to comply with industry best practices?
- A. Legal department
- B. Law enforcement
- C. Help desk
- D. Board member
Answer: A
Explanation:
The correct answer is C. Legal department.
According to the CompTIA Cybersecurity Analyst (CySA+) certification exam objectives, one of the tasks for a security analyst is to "report and escalate security incidents to appropriate stakeholders and authorities" 1. This includes reporting any inappropriate use of resources, such as installing cryptominers on workstations, which may violate the company's policies and cause financial and reputational damage. The legal department is the most appropriate group to escalate this issue to first, as they can advise on the legal implications and actions that can be taken against the employee. The legal department can also coordinate with other groups, such as law enforcement, help desk, or board members, as needed. The other options are not the best choices to escalate the issue to first, as they may not have the authority or expertise to handle the situation properly.
NEW QUESTION # 28
A security analyst is reviewing the logs of a web server and notices that an attacker has attempted to exploit a SQL injection vulnerability. Which of the following tools can the analyst use to analyze the attack and prevent future attacks?
- A. A network intrusion detection system
- B. A web proxy
- C. A vulnerability scanner
- D. A web application firewall
Answer: D
Explanation:
A web application firewall (WAF) is a tool that can protect web servers from attacks such as SQL injection, cross-site scripting, and other web-based threats. A WAF can filter, monitor, and block malicious HTTP traffic before it reaches the web server. A WAF can also be configured with rules and policies to detect and prevent specific types of attacks.
Reference:
1: CompTIA CySA+ Study Guide: Exam CS0-002, 2nd Edition : CompTIA CySA+ Certification Exam Objectives Version 4.0.pdf)
NEW QUESTION # 29
An analyst received an alert regarding an application spawning a suspicious command shell process Upon further investigation, the analyst observes the following registry change occurring immediately after the suspicious event:
Which of the following was the suspicious event able to accomplish?
- A. Establish persistence.
- B. Bypass file access controls.
- C. Impair defenses.
- D. Implement beaconing.
Answer: A
Explanation:
The suspicious event was able to accomplish establishing persistence by creating a registry change that runs a command shell process every time a user logs on. The registry change modifies the Userinit value under the HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon key, which specifies what programs should run when a user logs on to Windows. By appending "cmd.exe," to the existing value, the event ensures that a command shell process will be launched every time a user logs on, which can allow the attacker to maintain access to the system or execute malicious commands. The other options are not related to the registry change. Reference: CompTIA Cybersecurity Analyst (CySA+) Certification Exam Objectives (CS0-002), page 10; https://docs.microsoft.com/en-us/windows/win32/sysinfo/userinit-entry
NEW QUESTION # 30
Which of the following entities should an incident manager work with to ensure correct processes are adhered to when communicating incident reporting to the general public, as a best practice? (Select two).
- A. Legal
- B. Public relations
- C. Governance
- D. Law enforcement
- E. Human resources
- F. Manager
Answer: A,B
Explanation:
An incident manager should work with the legal and public relations entities to ensure correct processes are adhered to when communicating incident reporting to the general public, as a best practice. The legal entity can provide guidance on the legal implications and obligations of disclosing the incident, such as compliance with data protection laws, contractual obligations, and liability issues. The public relations entity can help craft the appropriate message and tone for the public communication, as well as manage the reputation and image of the organization in the aftermath of the incident. These two entities can help the incident manager balance the need for transparency and accountability with the need for confidentiality and security12. References: Incident Communication Templates, Incident Management: Processes, Best Practices & Tools - Atlassian
NEW QUESTION # 31
A cryptocurrency service company is primarily concerned with ensuring the accuracy of the data on one of its systems. A security analyst has been tasked with prioritizing vulnerabilities for remediation for the system.
The analyst will use the following CVSSv3.1 impact metrics for prioritization: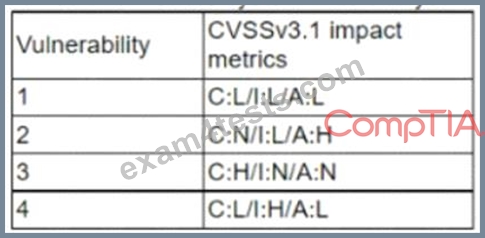
Which of the following vulnerabilities should be prioritized for remediation?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: B
Explanation:
Vulnerability 2 has the highest impact metrics, specifically the highest attack vector (AV) and attack complexity (AC) values. This means that the vulnerability is more likely to be exploited and more difficult to remediate.
References:
CVSS v3.1 Specification Document, section 2.1.1 and 2.1.2
The CVSS v3 Vulnerability Scoring System, section 3.1 and 3.2
NEW QUESTION # 32
During an investigation, an analyst discovers the following rule in an executive's email client:
The executive is not aware of this rule. Which of the following should the analyst do first to evaluate the potential impact of this security incident?
- A. Recommend that the management team implement SPF and DKIM.
- B. Remove the rule from the email client and change the password.
- C. Use the SIEM to correlate logging events from the email server and the domain server.
- D. Check the server logs to evaluate which emails were sent to <someaddress@domain,com>.
Answer: D
Explanation:
Checking the server logs to evaluate which emails were sent to <someaddress@domain,com> is the first action the analyst should do to evaluate the potential impact of this security incident. Server logs are records of events or activities that occur on a server, such as email transactions, web requests, or authentication attempts. Checking the server logs can help to determine how many emails were sent to <someaddress@domain,com>, when they were sent, who sent them, and what they contained. This can help to assess the scope and severity of the incident and plan further actions .
NEW QUESTION # 33
The developers recently deployed new code to three web servers. A daffy automated external device scan report shows server vulnerabilities that are failure items according to PCI DSS.
If the venerability is not valid, the analyst must take the proper steps to get the scan clean.
If the venerability is valid, the analyst must remediate the finding.
After reviewing the information provided in the network diagram, select the STEP 2 tab to complete the simulation by selecting the correct Validation Result and Remediation Action for each server listed using the drop-down options.
INTRUCTIONS:
The simulation includes 2 steps.
Step1:Review the information provided in the network diagram and then move to the STEP 2 tab.

STEP 2: Given the Scenario, determine which remediation action is required to address the vulnerability.
Answer:
Explanation:
NEW QUESTION # 34
A recent zero-day vulnerability is being actively exploited, requires no user interaction or privilege escalation, and has a significant impact to confidentiality and integrity but not to availability. Which of the following CVE metrics would be most accurate for this zero-day threat?
- A. CVSS:31/AV:K/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:L
- B. CVSS:31/AV:L/AC:L/PR:R/UI:R/S:U/C:H/I:L/A:H
- C. CVSS:31/AV:N/AC:L/PR:N/UI:H/S:U/C:L/I:N/A:H
- D. CVSS: 31/AV: N/AC: L/PR: N/UI: N/S: U/C: H/1: K/A: L
Answer: D
Explanation:
This answer matches the description of the zero-day threat. The attack vector is network (AV:N), the attack complexity is low (AC:L), no privileges are required (PR:N), no user interaction is required (UI:N), the scope is unchanged (S:U), the confidentiality and integrity impacts are high (C:H/I:H), and the availability impact is low (A:L). Official Reference: https://nvd.nist.gov/vuln-metrics/cvss
NEW QUESTION # 35
A managed security service provider is having difficulty retaining talent due to an increasing workload caused by a client doubling the number of devices connected to the network. Which of the following would best aid in decreasing the workload without increasing staff?
- A. EDR
- B. XDR
- C. SOAR
- D. SIEM
Answer: C
Explanation:
Explanation
SOAR stands for Security Orchestration, Automation and Response, which is a set of features that can help security teams manage, prioritize and respond to security incidents more efficiently and effectively. SOAR can help decrease the workload without increasing staff by automating repetitive tasks, streamlining workflows, integrating different tools and platforms, and providing actionable insights and recommendations. SOAR is also one of the current trends that CompTIA CySA+ covers in its exam objectives. Official References:
https://www.comptia.org/blog/the-new-comptia-cybersecurity-analyst-your-questions-answered
https://www.comptia.org/certifications/cybersecurity-analyst
https://partners.comptia.org/docs/default-source/resources/comptia-cysa-cs0-002-exam-objectives
NEW QUESTION # 36
A security analyst at a company called ACME Commercial notices there is outbound traffic to a host IP that resolves to https://offce365password.acme.co. The site's standard VPN logon page is
www.acme.com/logon. Which of the following is most likely true?
- A. A social engineering attack is underway
- B. This is a normal password change URL.
- C. The security operations center is performing a routine password audit.
- D. A new VPN gateway has been deployed
Answer: A
Explanation:
A social engineering attack is underway is the most likely explanation for the outbound traffic to a host IP that resolves to https://offce365password.acme.co, while the site's standard VPN logon page is www.acme.com/logon. A social engineering attack is a technique that exploits human psychology and behavior to manipulate people into performing actions or divulging information that benefit the attackers. A common type of social engineering attack is phishing, which involves sending fraudulent emails or other messages that appear to come from a legitimate source, such as a company or a colleague, and lure the recipients into clicking on malicious links or attachments, or entering their credentials or other sensitive information on fake websites. In this case, the attackers may have registered a domain name that looks similar to the company's domain name, but with a typo (offce365 instead of office365), and set up a fake website that mimics the company's VPN logon page. The attackers may have also sent phishing emails to the company's employees, asking them to reset their passwords or log in to their VPN accounts using the malicious link. The security analyst should investigate the source and content of the phishing emails, and alert the employees not to click on any suspicious links or enter their credentials on any untrusted websites. Official Reference:
https://partners.comptia.org/docs/default-source/resources/comptia-cysa-cs0-002-exam-objectives
https://www.comptia.org/certifications/cybersecurity-analyst
https://www.comptia.org/blog/the-new-comptia-cybersecurity-analyst-your-questions-answered
NEW QUESTION # 37
An organization conducted a web application vulnerability assessment against the corporate website, and the following output was observed:
Which of the following tuning recommendations should the security analyst share?
- A. Configure an Access-Control-Allow-Origin header to authorized domains
- B. Set an HttpOnlvflaq to force communication by HTTPS
- C. Block requests without an X-Frame-Options header
- D. Disable the cross-origin resource sharing header
Answer: C
Explanation:
The output shows that the web application is vulnerable to clickjacking attacks, which allow an attacker to overlay a hidden frame on top of a legitimate page and trick users into clicking on malicious links. Blocking requests without an X-Frame-Options header can prevent this attack by instructing the browser to not display the page within a frame.
NEW QUESTION # 38
An organization was compromised, and the usernames and passwords of all em-ployees were leaked online.
Which of the following best describes the remedia-tion that could reduce the impact of this situation?
- A. System hardening
- B. Multifactor authentication
- C. Password changes
- D. Password encryption
Answer: B
Explanation:
Explanation
Multifactor authentication (MFA) is a security method that requires users to provide two or more pieces of evidence to verify their identity, such as a password, a PIN, a fingerprint, or a one-time code. MFA can reduce the impact of a credential leak because even if the attackers have the usernames and passwords of the employees, they would still need another factor to access the organization's systems and resources. Password changes, system hardening, and password encryption are also good security practices, but they do not address the immediate threat of compromised credentials.
References: CompTIA CySA+ Certification Exam Objectives, [What Is Multifactor Authentication (MFA)?]
NEW QUESTION # 39
A security analyst performs a vulnerability scan. Based on the metrics from the scan results, the analyst must prioritize which hosts to patch. The analyst runs the tool and receives the following output: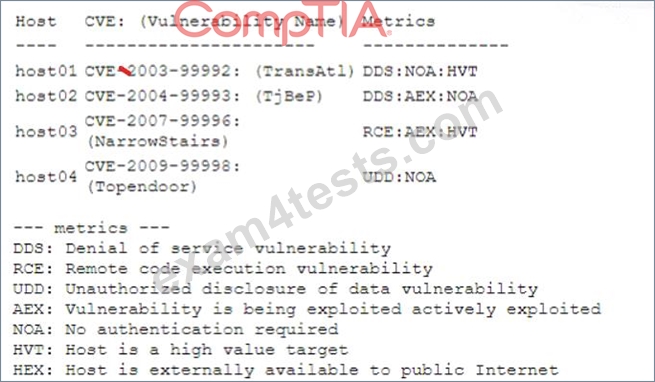
Which of the following hosts should be patched first, based on the metrics?
- A. host02
- B. host03
- C. host04
- D. host01
Answer: B
Explanation:
Host03 should be patched first, based on the metrics, as it has the highest risk score and the highest number of critical vulnerabilities. The risk score is calculated by multiplying the CVSS score by the exposure factor, which is the percentage of systems that are vulnerable to the exploit. Host03 has a risk score of 10 x 0.9 = 9, which is higher than any other host. Host03 also has 5 critical vulnerabilities, which are the most severe and urgent to fix, as they can allow remote code execution, privilege escalation, or data loss. The other hosts have lower risk scores and lower numbers of critical vulnerabilities, so they can be patched later.
NEW QUESTION # 40
A company is deploying new vulnerability scanning software to assess its systems. The current network is highly segmented, and the networking team wants to minimize the number of unique firewall rules. Which of the following scanning techniques would be most efficient to achieve the objective?
- A. Deploy a scanner sensor on every segment and perform credentialed scans.
- B. Deploy a central scanner and perform non-credentialed scans.
- C. Deploy agents on all systems to perform the scans.
- D. Deploy a cloud-based scanner and perform a network scan.
Answer: C
Explanation:
USB ports are a common attack vector that can be used to deliver malware, steal data, or compromise systems. The first step to mitigate this vulnerability is to check the configurations of the company assets and disable or restrict the USB ports if possible. This will prevent unauthorized devices from being connected and reduce the attack surface. The other options are also important, but they are not the first priority in this scenario.
Reference:
CompTIA CySA+ CS0-003 Certification Study Guide, page 247
What are Attack Vectors: Definition & Vulnerabilities, section "How to secure attack vectors" Are there any attack vectors for a printer connected through USB in a Windows environment?, answer by user "schroeder"
NEW QUESTION # 41
Which of the following is the first step that should be performed when establishing a disaster recovery plan?
- A. Identity applications to be run during a disaster
- B. Determine the site to be used during a disaster
C Demonstrate adherence to a standard disaster recovery process - C. Agree on the goals and objectives of the plan
Answer: C
Explanation:
Explanation
The first step that should be performed when establishing a disaster recovery plan is to agree on the goals and objectives of the plan. The goals and objectives of the plan should define what the plan aims to achieve, such as minimizing downtime, restoring critical functions, ensuring data integrity, or meeting compliance requirements. The goals and objectives of the plan should also be aligned with the business needs and priorities of the organization and be measurable and achievable.
NEW QUESTION # 42
Which of the following is the greatest security concern regarding ICS?
- A. Issues on the systems cannot be reversed without rebuilding the systems.
- B. The involved systems are generally hard to identify.
- C. The systems are configured for automatic updates, leading to device failure.
- D. The systems are oftentimes air gapped, leading to fileless malware attacks.
Answer: A
Explanation:
Industrial control systems (ICS) are systems that monitor and control physical processes, such as power generation, water treatment, manufacturing, and transportation. ICS are often critical for public safety and national security, and therefore a prime target for cyberattacks. One of the greatest security concerns regarding ICS is that issues on the systems cannot be reversed without rebuilding the systems. This means that any damage or disruption caused by an attack can have long-lasting and catastrophic consequences for the physical infrastructure and human lives. The other options are not true or not specific to ICS. Reference: CompTIA Cybersecurity Analyst (CySA+) Certification Exam Objectives (CS0-002), page 13; https://www.us-cert.gov/ics/What-are-Industrial-Control-Systems
NEW QUESTION # 43
......
CompTIA CS0-003 (CompTIA Cybersecurity Analyst (CySA+) Certification) Exam is designed to assess the knowledge and skills of candidates in the field of cybersecurity analysis. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification exam is an esteemed qualification for cybersecurity analysts and is globally recognized in the industry. It is an intermediate-level certification, which means that candidates are required to have some prior knowledge and experience in this field before attempting the exam.
Earning the CompTIA CySA+ certification demonstrates to employers that an individual has the knowledge and skills required to analyze and respond to security threats in a fast-paced and constantly evolving cybersecurity landscape. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is recognized globally and can help individuals stand out in a competitive job market. In addition, the certification is a prerequisite for several advanced cybersecurity certifications, such as the CompTIA Advanced Security Practitioner (CASP+) and the Certified Information Systems Security Professional (CISSP) certifications.
Pass Your CS0-003 Exam Easily With 100% Exam Passing Guarantee: https://www.exam4tests.com/CS0-003-valid-braindumps.html
CS0-003 Dumps are Available for Instant Access: https://drive.google.com/open?id=1kIWSMkbC9iUO3HYnuMMVmBDFvPf0K5GL